CMMC Level 1 Self-Assessment Template: A Plain-English Guide for Small Contractors

If you sell to the Department of Defense, or to a prime contractor that does, someone has probably asked you about CMMC by now. For most small businesses that only handle Federal Contract Information (FCI), the answer is CMMC Level 1: a yearly self-assessment you complete yourself and then affirm in the government’s Supplier Performance Risk System (SPRS). No outside assessor is required, but you still need to do it properly and be able to show your work.
This guide walks through what a CMMC Level 1 self-assessment covers, how to run one in a few focused sessions, and what a good self-assessment template should include so you are not starting from a blank page.
What CMMC Level 1 actually requires
CMMC Level 1 is built on the 15 basic safeguarding requirements in FAR 52.204-21. The official CMMC Level 1 assessment guide breaks them into 17 practices across six areas:
- Access Control (AC): limit system access to authorized users and devices, control what they can do, verify external connections, and keep FCI off public websites.
- Identification and Authentication (IA): identify users and devices, and authenticate them before granting access.
- Media Protection (MP): sanitize or destroy media holding FCI before disposal or reuse.
- Physical Protection (PE): limit physical access, escort visitors, keep visitor logs and control physical access devices such as keys and badges.
- System and Communications Protection (SC): monitor and protect your network boundary, and separate publicly accessible systems from internal networks.
- System and Information Integrity (SI): fix flaws promptly, protect against malicious code, keep protections updated and run scans.
Each practice has assessment objectives, which are the specific things you must be able to show are in place. At Level 1, every practice must be fully met. There is no partial credit and no plan of action to finish items later, which is why a careful self-assessment matters.
Step 1: Scope what is in and out
Before you score anything, decide which people, devices, systems and locations touch FCI. Typical examples are the laptops your team uses for contract work, your email and file sharing service, and the office where paperwork is kept. A tight, written scope keeps the assessment manageable and makes your answers easier to defend.
This is also when you confirm whether you handle Controlled Unclassified Information (CUI). If you do, Level 1 is probably not enough and you will likely need Level 2. Check your contracts and ask your prime if you are unsure.
Step 2: Score each practice against its objectives
Go practice by practice and mark each assessment objective as MET or NOT MET. Write one or two sentences on how you meet it, such as “all staff sign in with unique accounts and multi-factor authentication.” Vague answers like “we’re secure” will not hold up if a prime or the government asks questions later.
Step 3: Gather evidence as you go
For every MET answer, note the proof: a screenshot of your account list, your antivirus console, a visitor log, a media disposal record or a short written policy. Keep it in one folder organized by practice. Evidence collected during the assessment is far easier than evidence hunted down months later.
Step 4: Fix gaps, then affirm in SPRS
Anything marked NOT MET has to be fixed before you affirm. Common quick fixes include turning on automatic updates, removing old user accounts, starting a visitor log and writing down how you dispose of old drives. Once everything is met, enter your results in SPRS and have a senior official affirm compliance. You repeat the self-assessment and affirmation every year.
What a good CMMC Level 1 self-assessment template includes
A spreadsheet with 17 rows is a start, but it leaves you guessing about scope, evidence and the SPRS steps. A useful template kit should give you:
- A scoping worksheet to separate FCI from CUI and list in-scope assets.
- A self-assessment workbook covering all 17 practices with every assessment objective and a MET or NOT MET score for each.
- An evidence checklist per practice, so you know exactly what proof to save.
- Short policies for the six practice areas, written so a small team can actually follow them.
- A step-by-step guide for SPRS entry and the annual affirmation.
- Simple logs for visitors, media sanitization, access reviews and keys.
Get the CMMC Level 1 Kit
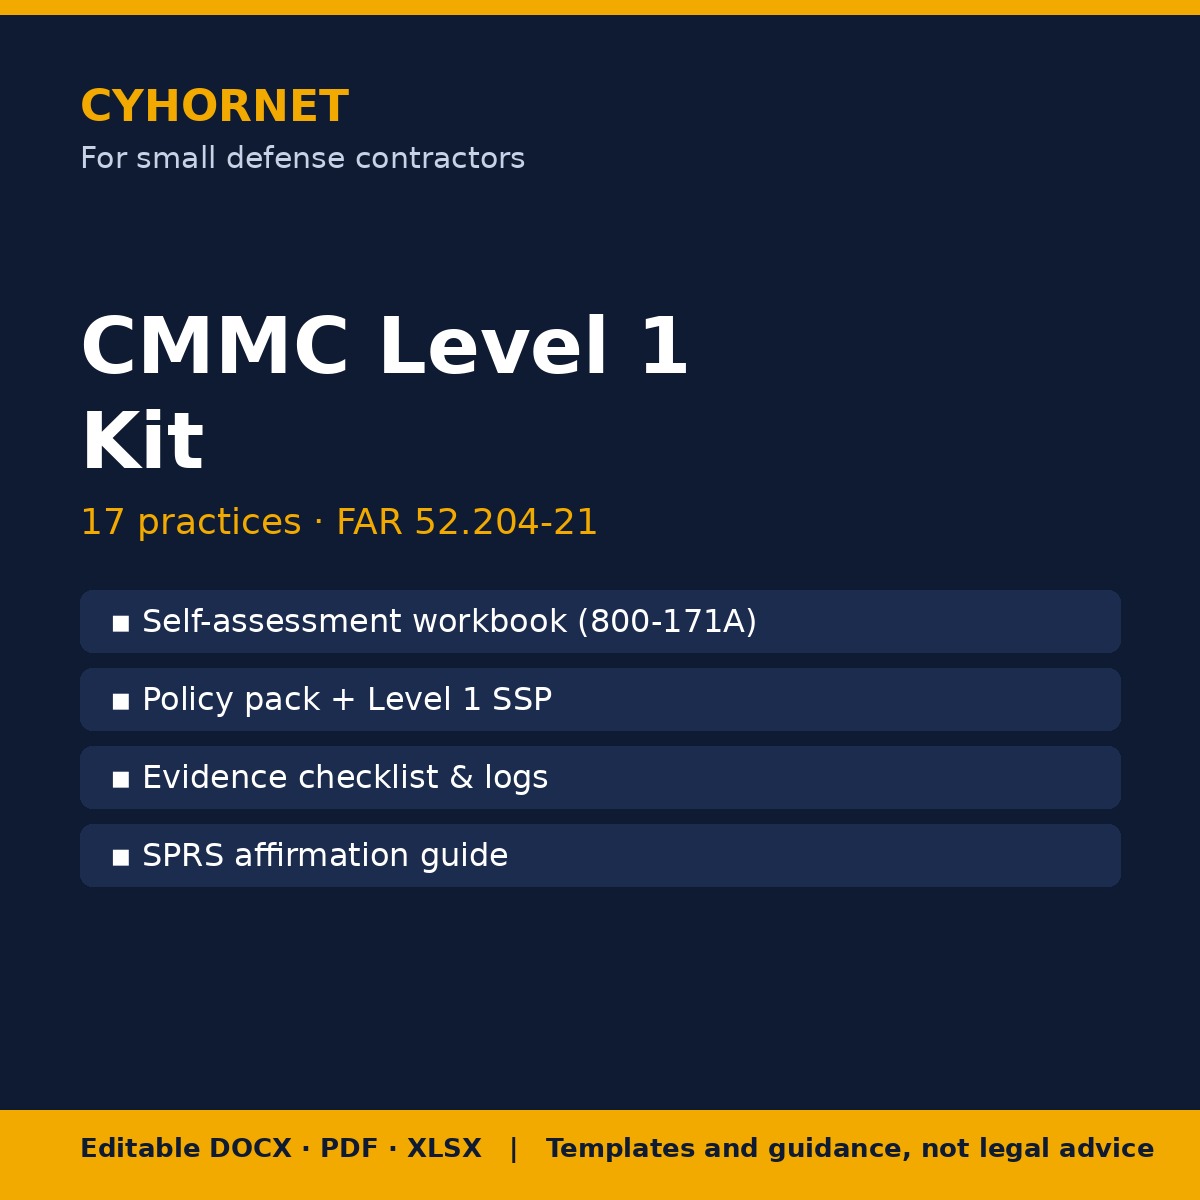
The CMMC Level 1 Kit from cyhornet.ai includes everything on that list: a scoping worksheet, a 17-practice self-assessment workbook with NIST SP 800-171A objectives, MET or NOT MET dropdowns and an automatic summary, an evidence checklist per practice, a lightweight Level 1 System Security Plan, a policy pack for AC, IA, MP, PE, SC and SI, an SPRS entry and annual affirmation guide, a prime questionnaire answer library, a “Do you need Level 2?” decision tree, and ready-to-use logs. Files are editable Word and Excel plus PDFs, delivered as an instant download.
Want an expert alongside you? The CMMC Level 1 Done-with-you Review adds two 90-minute remote working sessions with a Cyhornet GRC analyst for organizations with up to 10 staff. You finish with a completed workbook, an evidence gaps list with a 30-day fix plan, and preparation for your senior official’s affirmation. If a prime has sent you a long security questionnaire, see Prime Security Questionnaire Answers, and if you also need an AI policy, the AI Policy Pro and CMMC Level 1 Kit bundle covers both.
Not ready to buy? Start with the free Security Questionnaire Response Prep Checklist and the free Employee Offboarding Access Removal Checklist, which helps with the access control practices. For more guides, visit the cyhornet.ai blog, including our AI acceptable use policy guide for small business.
Frequently asked questions
Does a CMMC Level 1 self-assessment certify my business?
No. Level 1 is a self-assessment that you complete and a senior official affirms in SPRS. A template kit helps you do it properly, but it does not certify you.
How often do I need to do it?
Every year. You complete a new self-assessment and submit a new affirmation in SPRS annually.
Can I leave some practices unfinished and fix them later?
No. At Level 1 every practice must be fully met before you affirm. Fix gaps first, then affirm.
What if my company handles CUI?
You likely need CMMC Level 2. The CMMC Level 1 Kit includes a decision tree to help you check, and the Done-with-you Review can help you decide.
What format are the templates?
Editable DOCX and XLSX files plus PDFs, delivered as an instant ZIP download.
General information only, not legal advice. Templates and guidance do not certify or guarantee compliance with any law, regulation or framework. Cyhornet LLC is not a law firm and is not affiliated with NIST, DoD or any government agency.