When a client asks for your AI or security policy, don’t start from scratch.
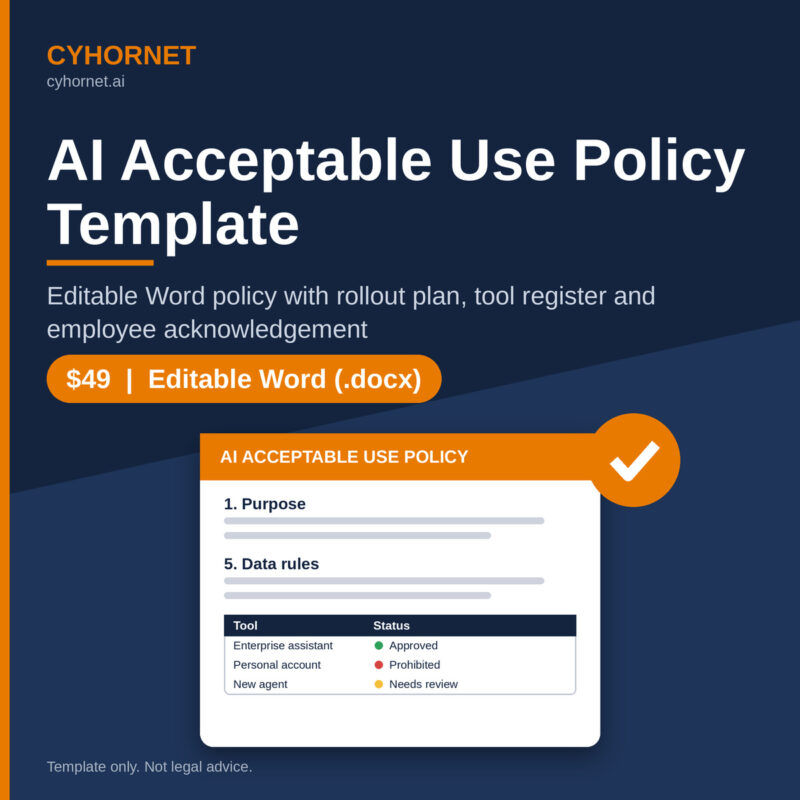
Get a free 30-day checklist by email. Then use our editable policy template — approved tools, data that should never go into AI, and who reviews exceptions — or have us write it for you.
Practical AI governance & SOC 2 templates, built by a GRC practitioner
Cyhornet helps startups and growing businesses achieve SOC 2, ISO 27001, NIST, and AI governance readiness by combining compliance expertise with automation.
Choose your path
Free SOC 2 readiness checklist
Find your gaps before you talk to an auditor.
Get the free checklistDIY automation pack
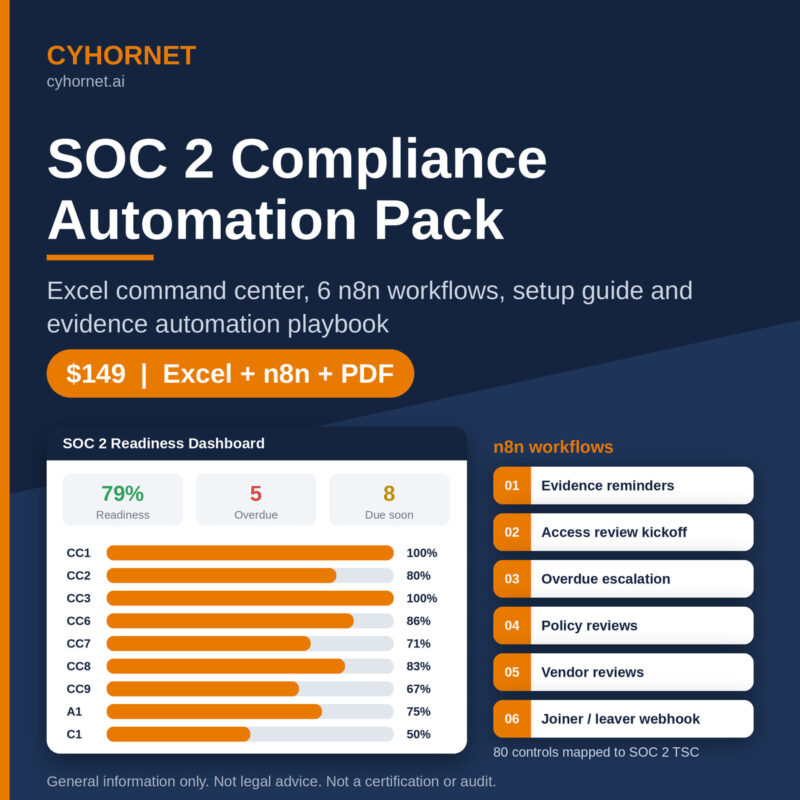
Editable control workbook plus six n8n workflows and setup guides.
View the packTemplates and setup help prepare you for an audit; they are not a SOC 2 report. Auditor fees are separate.
Featured: GRC & AI Governance Templates
Designed for Clarity
Compliance shouldn't feel like guesswork. Cyhornet gives startups and growing businesses clear, ready-to-use templates for SOC 2, ISO 27001, NIST and AI governance, so you know exactly what to do next.
Every kit is built from real-world security and compliance program experience, so you can skip the blank page and move straight to audit-ready work.
Built With Purpose
We focus on practical, organized systems for risk management, vendor reviews and responsible AI use, not generic tools or short-term hype.
Our goal is simple: help you earn trust, pass reviews and grow with confidence.
What You Can Do
Practical tools and services for security, compliance and AI governance.
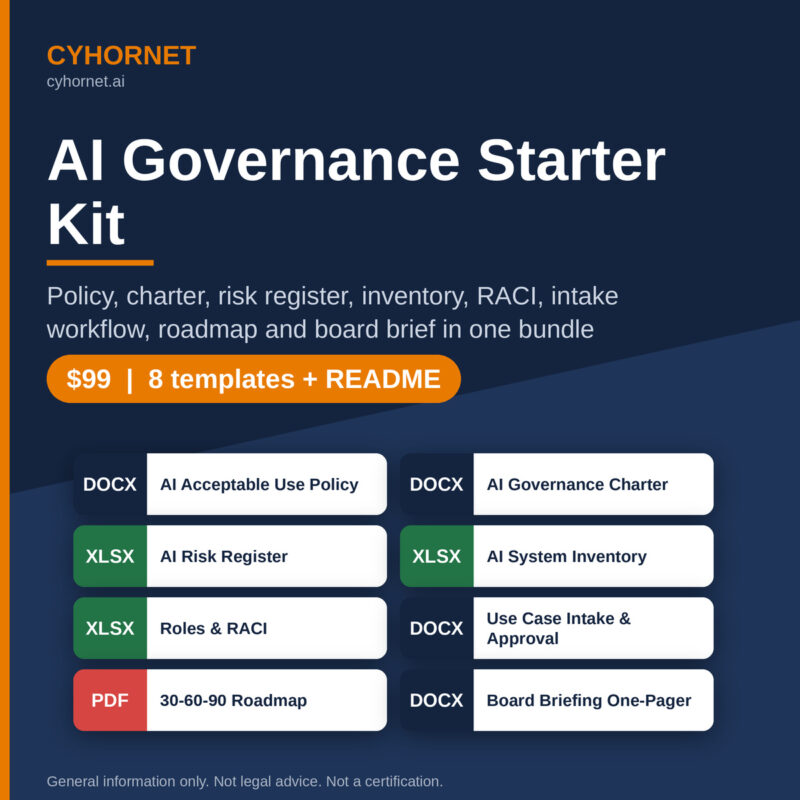
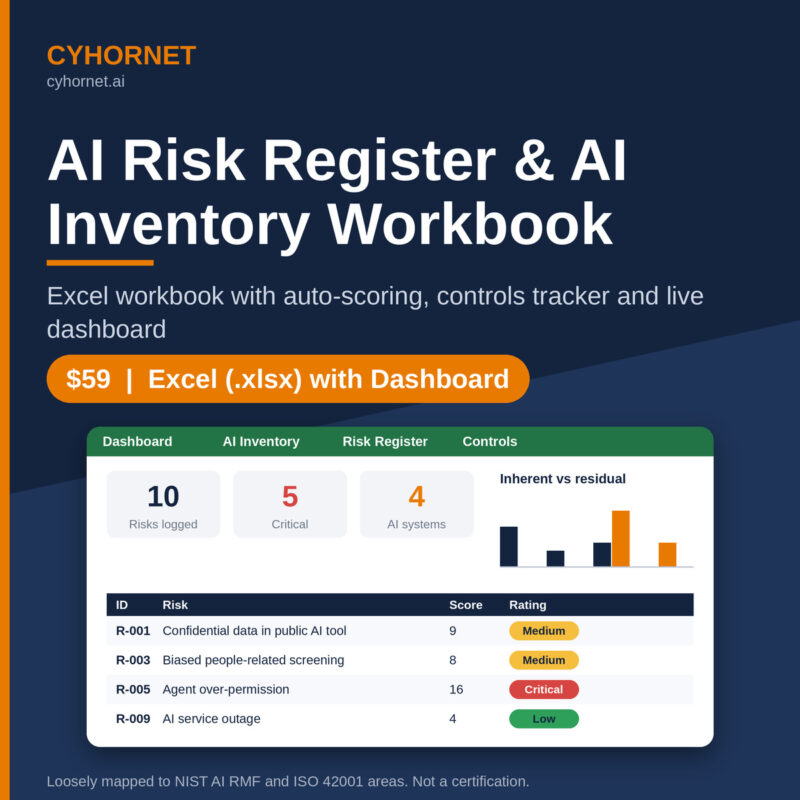
GRC & AI Governance Kits
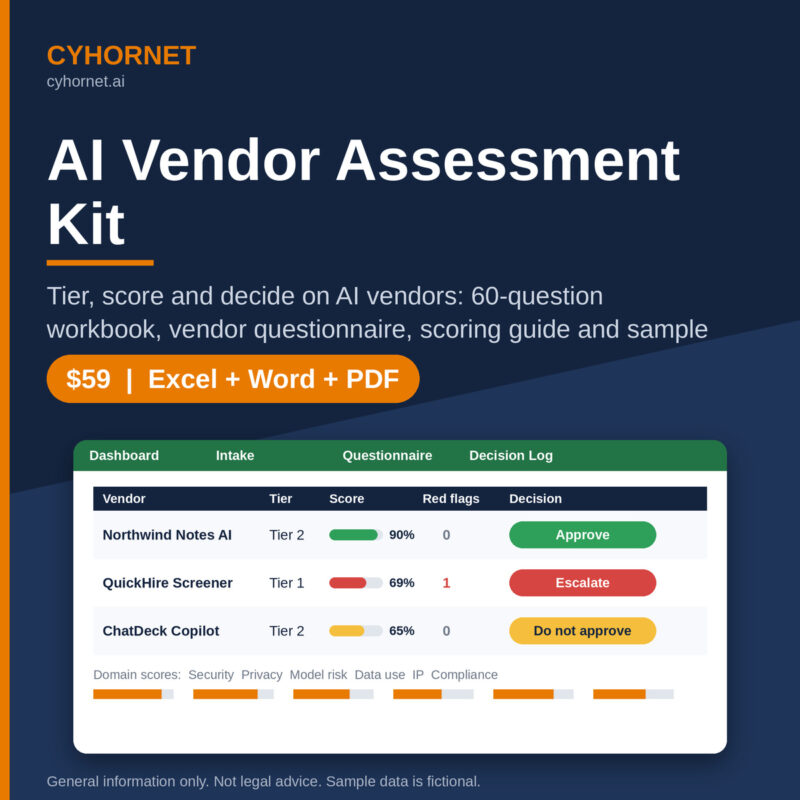
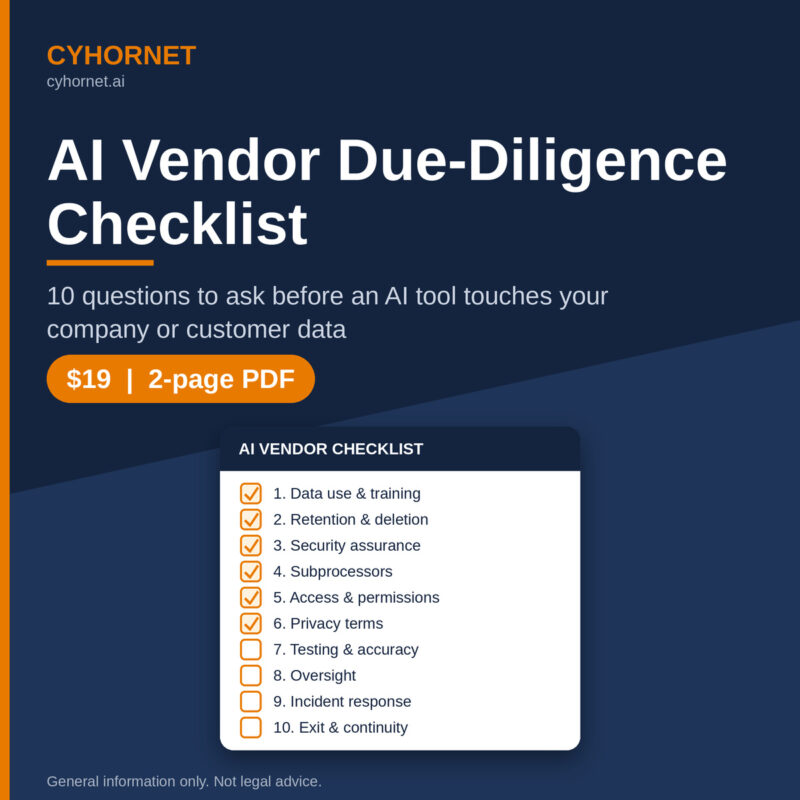
Ready-to-use policies, risk registers, control trackers and automation workflows for SOC 2, ISO 27001, NIST and AI governance.
Readiness Assessments & Advisory
Focused SOC 2, ISO 27001, NIST, AI governance and vendor risk assessments, with a clear plan for what to fix first.
White-Label Templates
Brand our GRC and AI governance kits as your own and deliver them to your clients. Built for consultants, vCISOs and MSPs.
How Cyhornet Works
Three steps to audit-ready.
Pick your starting point
Choose a ready-made GRC or AI governance kit, or book a free call to scope an assessment.
Tailor it to your organization
Adapt the policies, controls and workflows to your systems, risks and audit goals.
Get audit-ready and stay that way
Put the controls in place, collect evidence, and keep improving as you grow.
Who Cyhornet Is For
Startups, SaaS teams, and growing businesses that need to prepare for SOC 2, ISO 27001, NIST, or AI governance without hiring a full compliance team.
If you're facing your first audit, answering security questionnaires, or putting AI policies in place, we give you a clear, practical path to audit-ready.
Why Cyhornet Is Different
Our kits and assessments are built by GRC practitioners with hands-on experience leading security, risk, and compliance programs, including FedRAMP and NIST work.
Every template is editable, mapped to real frameworks, and ready to use. No fluff and no bloated tools, just the policies, registers, and checklists auditors actually ask for, plus advisory support when you need it.