Scope SOC 2 first, so you build only what your report needs
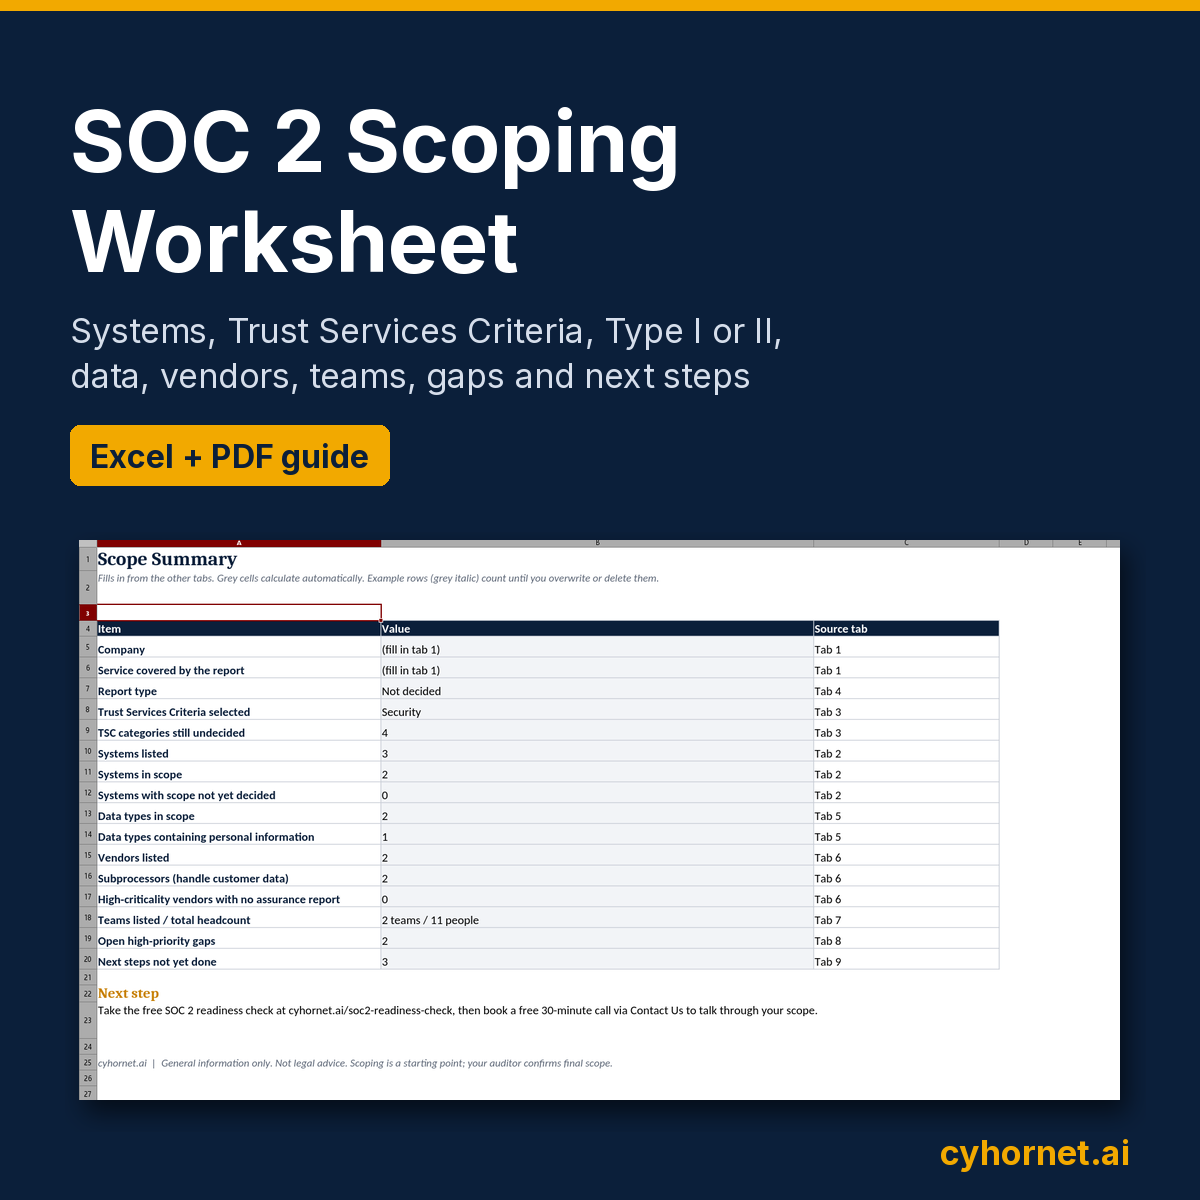
A SOC 2 report describes one system: the service your customers rely on, plus the people, processes, technology and vendors behind it. Teams that skip scoping often take on work buyers never asked for, or end up with a report that doesn’t answer their customers’ questions. This worksheet gives you a structured way to agree on scope as a team.
What’s inside
- Instructions: what each tab is for, the order to fill it in, and what the cell colours mean.
- 1. Company & Drivers: the service the report covers, why you’re pursuing SOC 2, and who is asking for it.
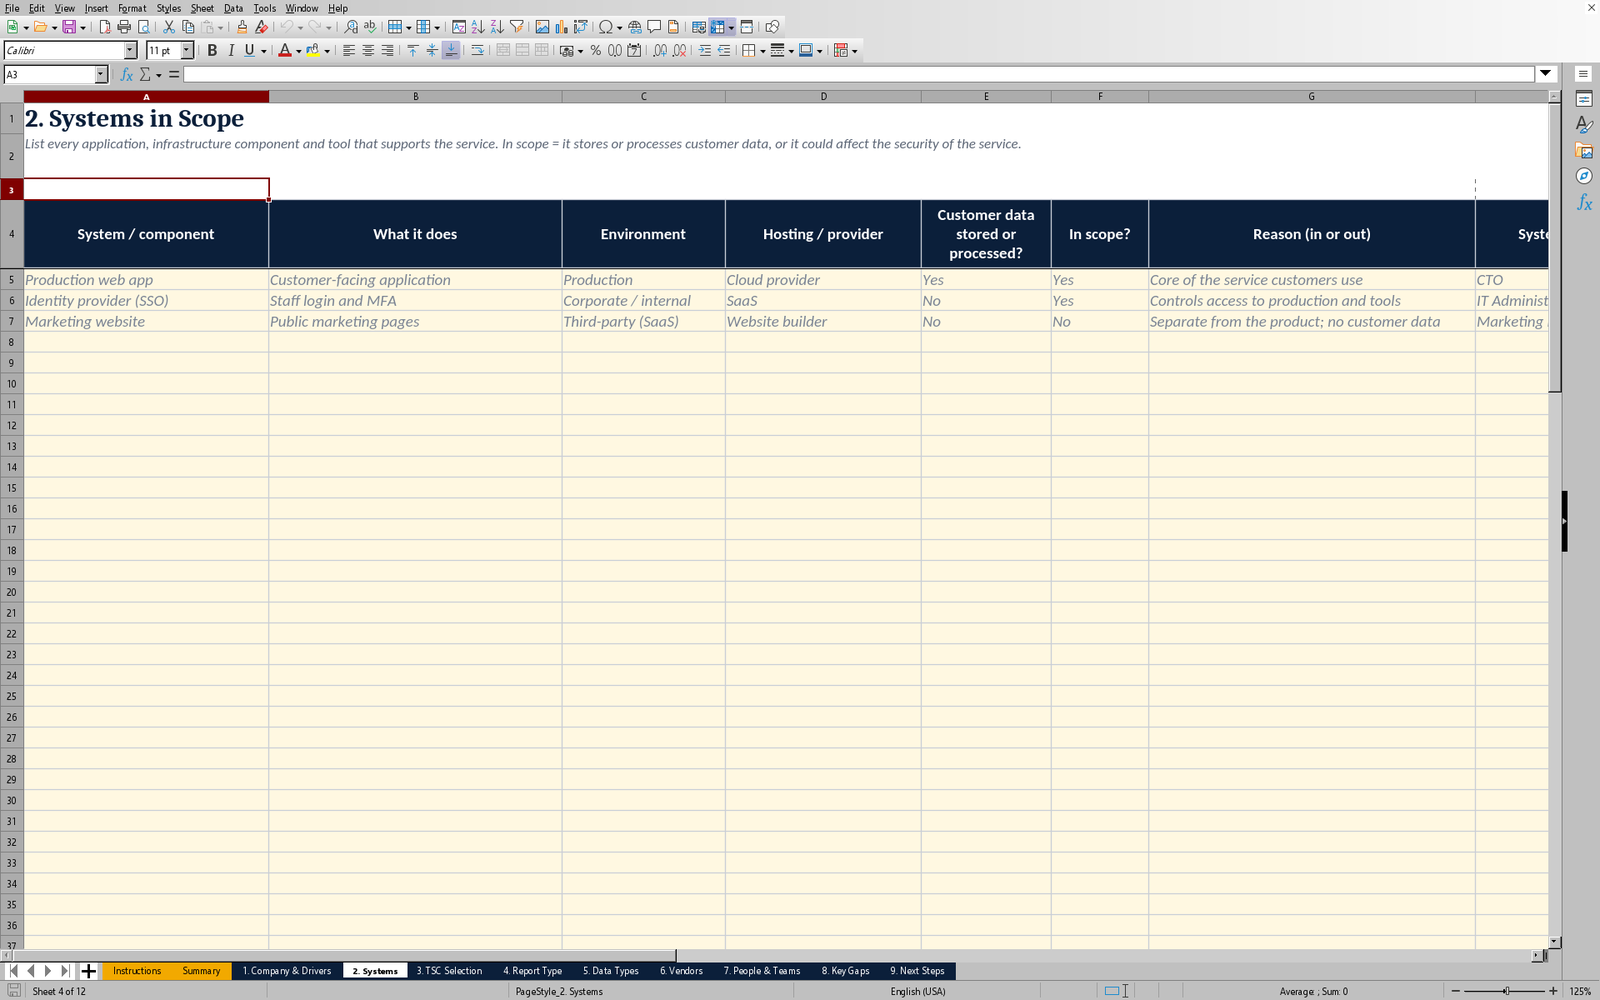
- 2. Systems: every application, infrastructure component and tool, with an in-scope or out-of-scope decision and the reason.
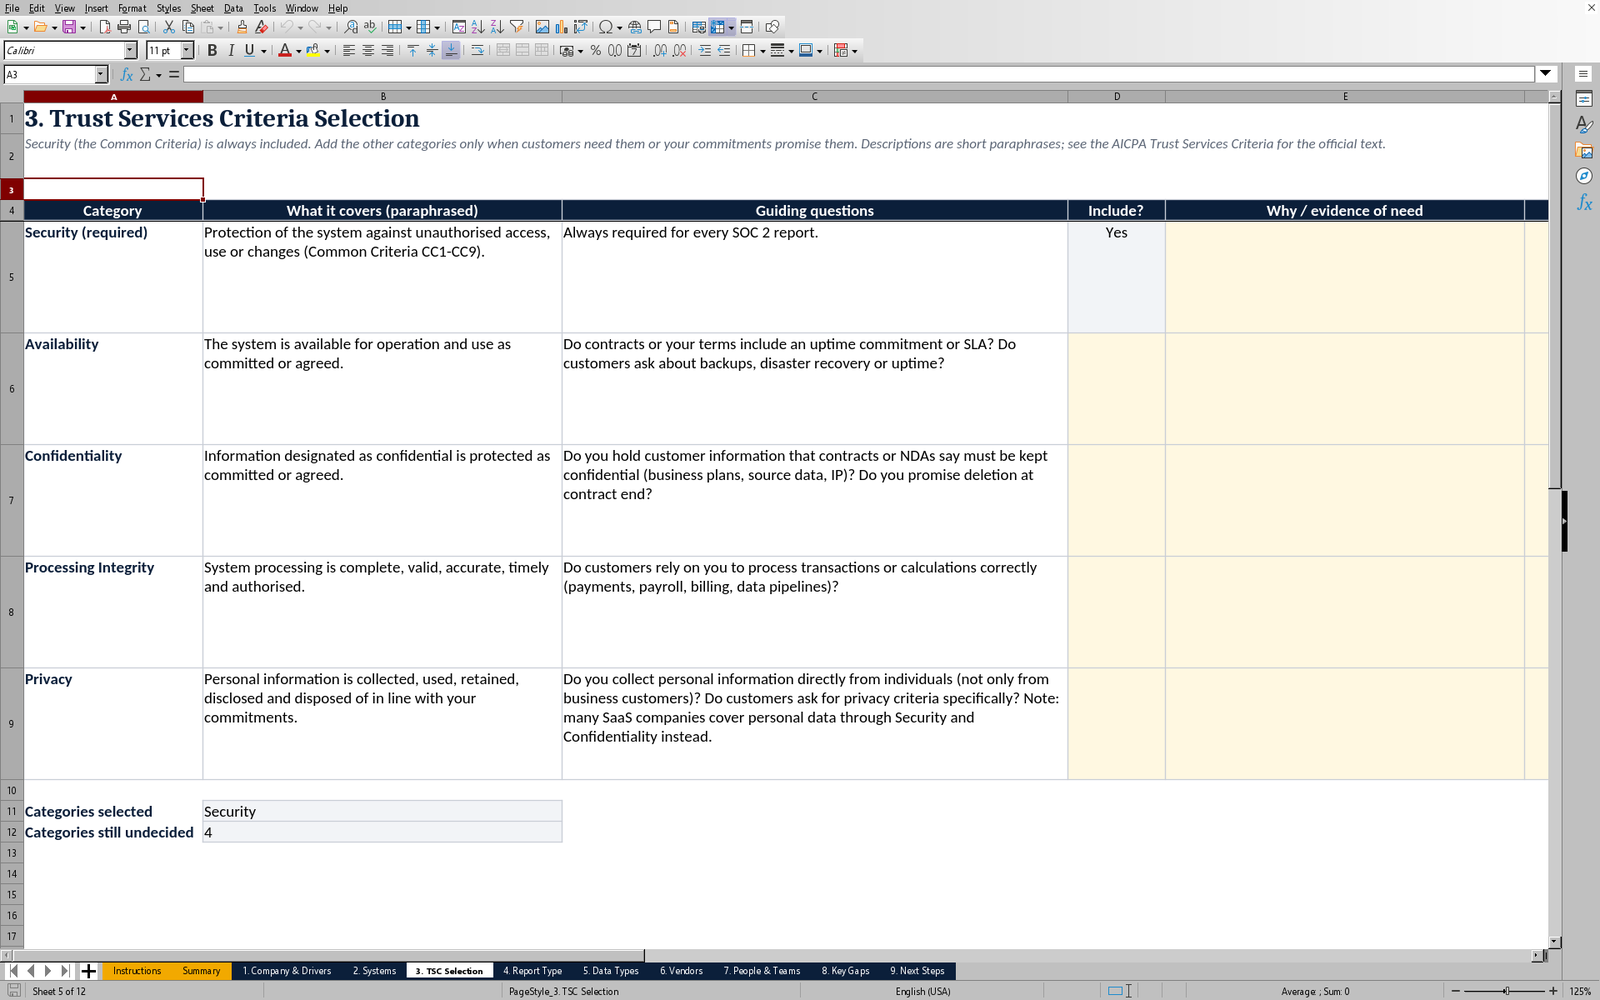
- 3. Trust Services Criteria: Security is always included. Guiding questions help you decide on Availability, Confidentiality, Processing Integrity and Privacy.
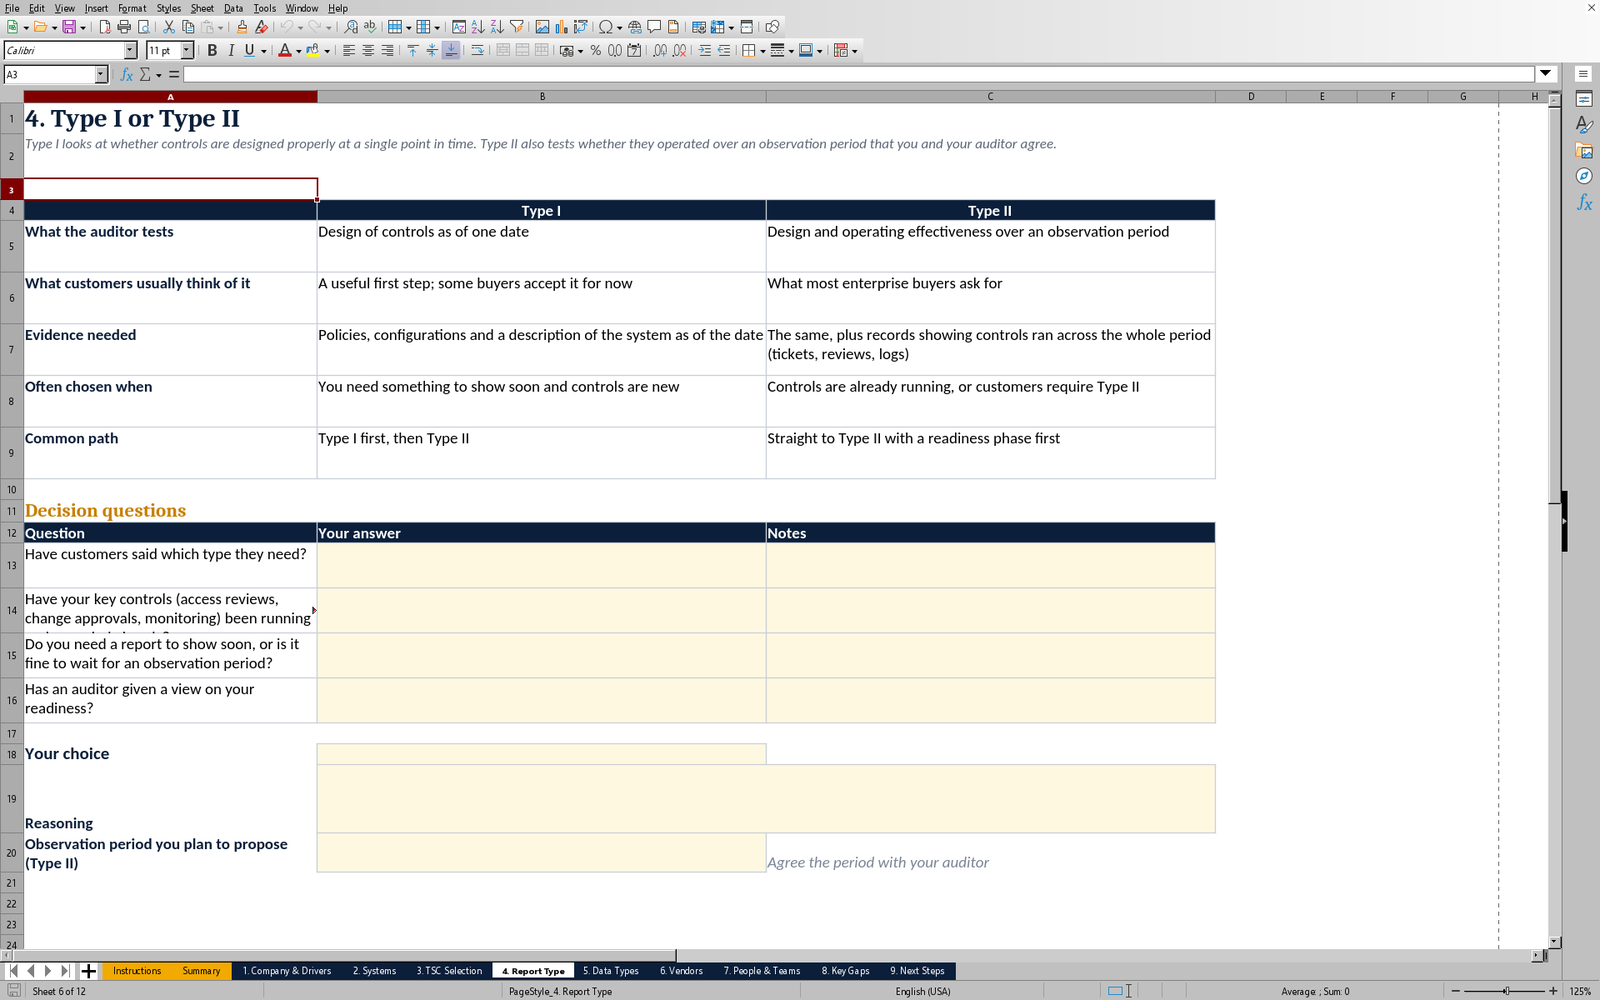
- 4. Report Type: a side-by-side comparison of Type I and Type II, with decision questions and a place to record your choice.
- 5. Data Types: what data the service handles, how sensitive it is, and where it lives.
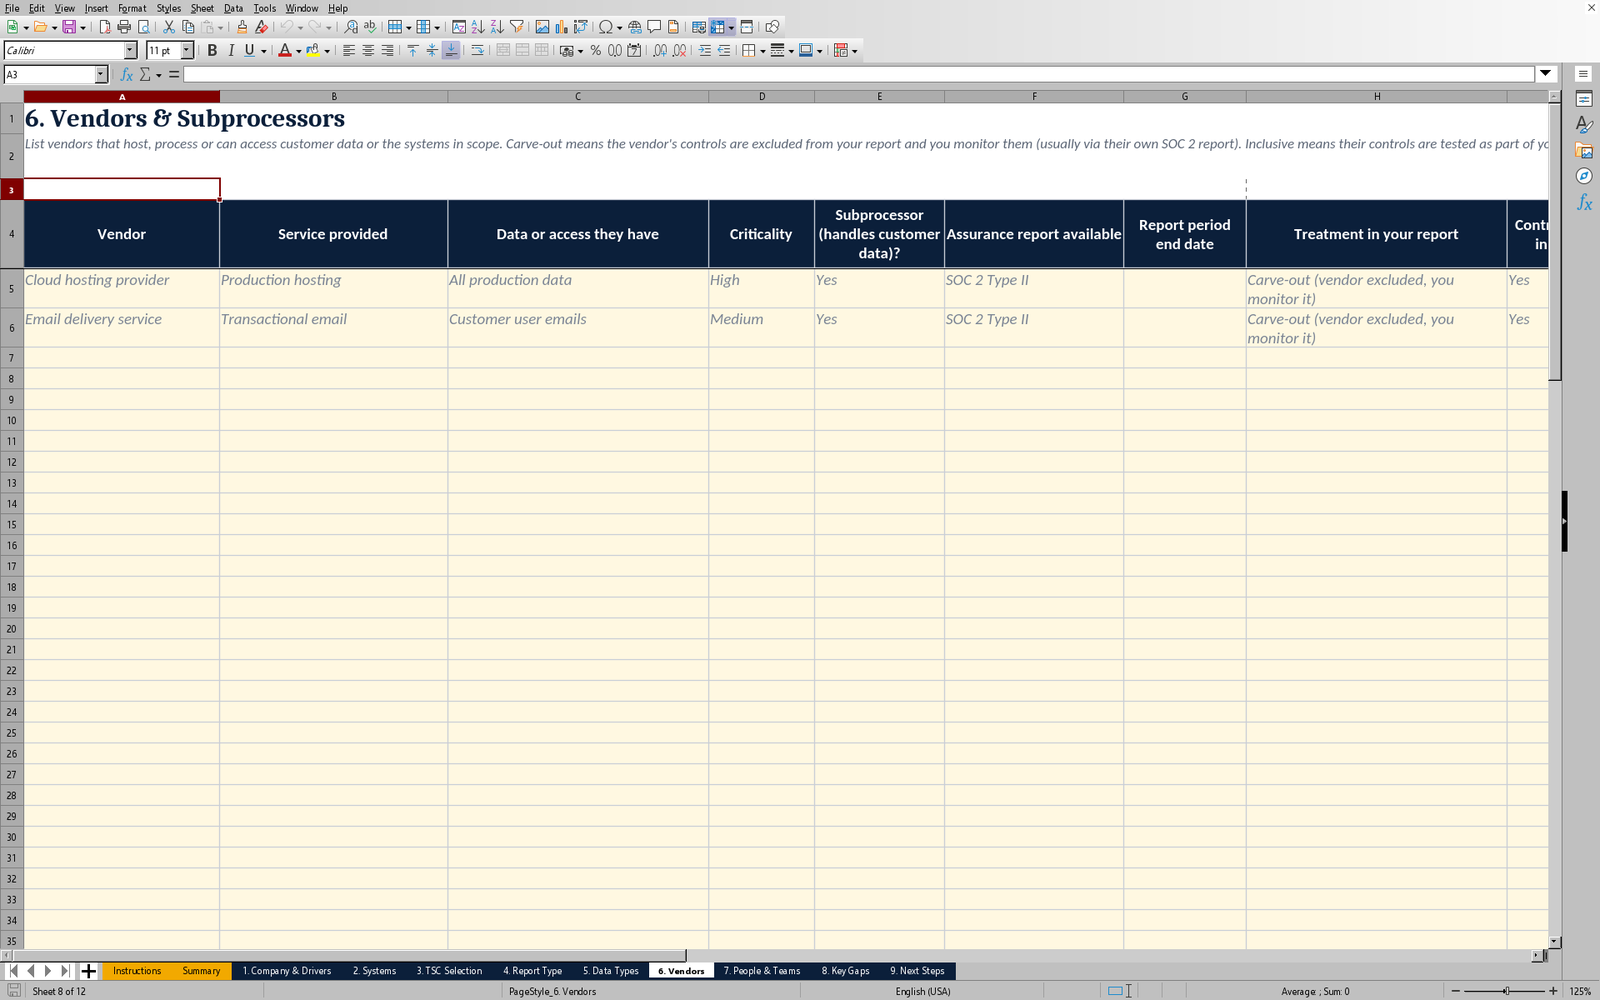
- 6. Vendors & Subprocessors: the data or access each vendor has, its assurance report, and whether it is carved out or included.
- 7. People & Teams: who builds, runs and supports the system, including contractors.
- 8. Key Gaps and 9. Next Steps: what you already know is missing, turned into owned actions.
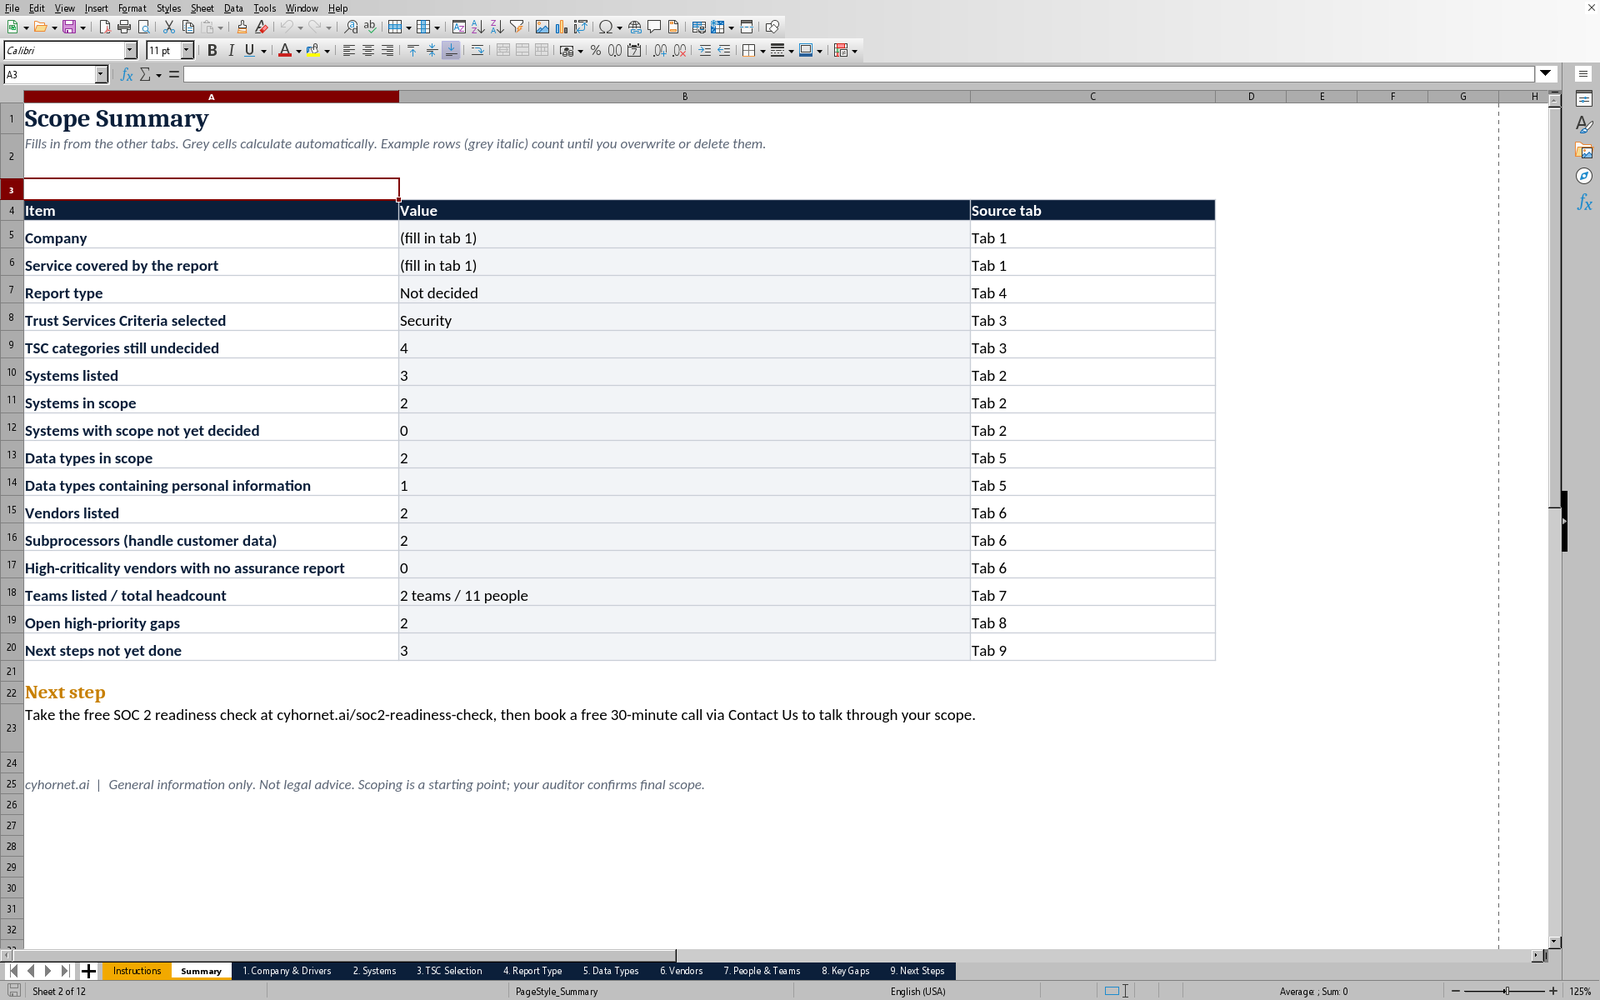
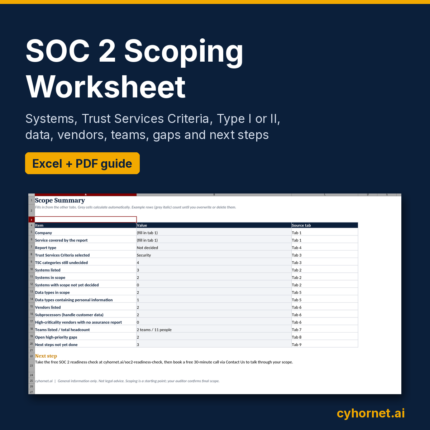
- Summary: fills in automatically. Use it to confirm scope with leadership and brief an auditor.
- PDF guide: a short how-to covering scoping tips, TSC selection and Type I vs Type II.
Who it’s for
Founders, CTOs and security or compliance leads at small SaaS and service companies who are starting SOC 2 and want a clear scope before choosing tools, consultants or an auditor.
What it doesn’t do
This is a planning worksheet. It doesn’t make you SOC 2 compliant, certify anything, or replace an independent CPA firm, which alone can examine your controls and issue a SOC 2 report. Your auditor confirms the final scope. Trust Services Criteria descriptions are short paraphrases; refer to the AICPA criteria for the official text.
Next step
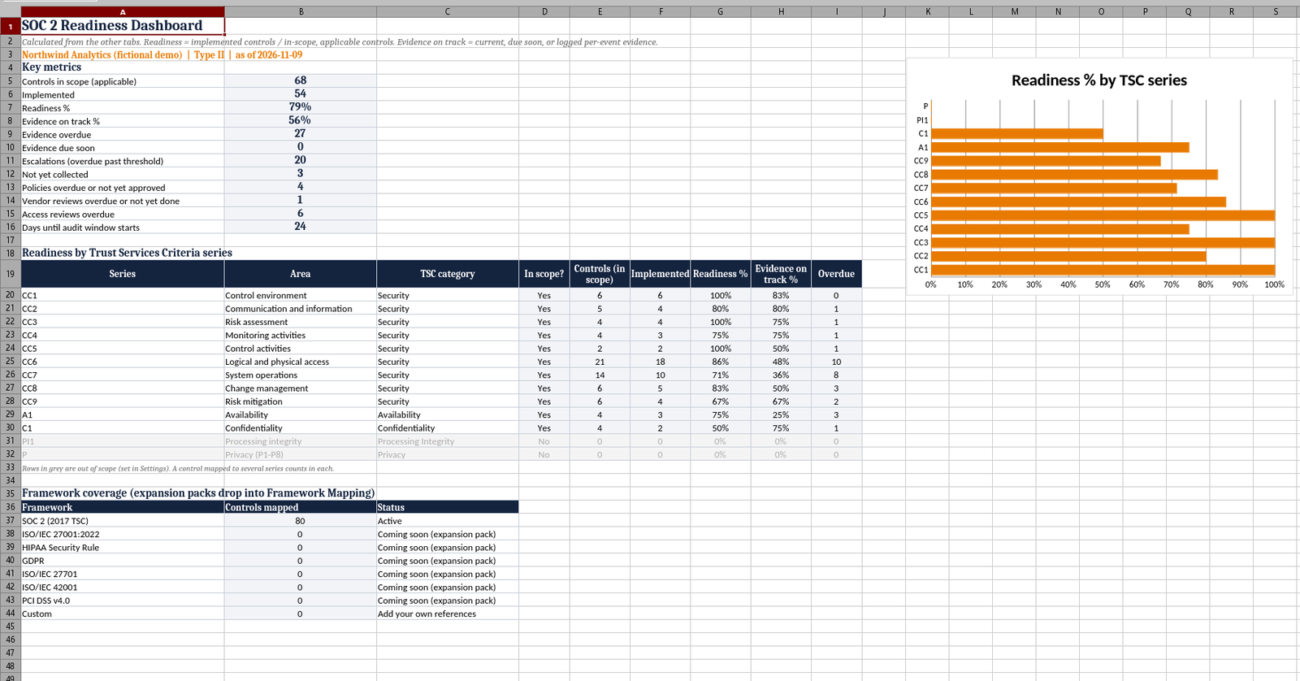
Take the free SOC 2 readiness check. If you’d like to talk through your scope, book a free 30-minute call through Contact Us. When you’re ready to track controls and evidence, see the SOC 2 Compliance Automation Pack.
General information only. Not legal advice. © Cyhornet LLC. Licensed for use within your own organisation.